 Spend by Product Exec
Solutions for teams · IT, security and audit
A system your auditors and your security team can both sign off.
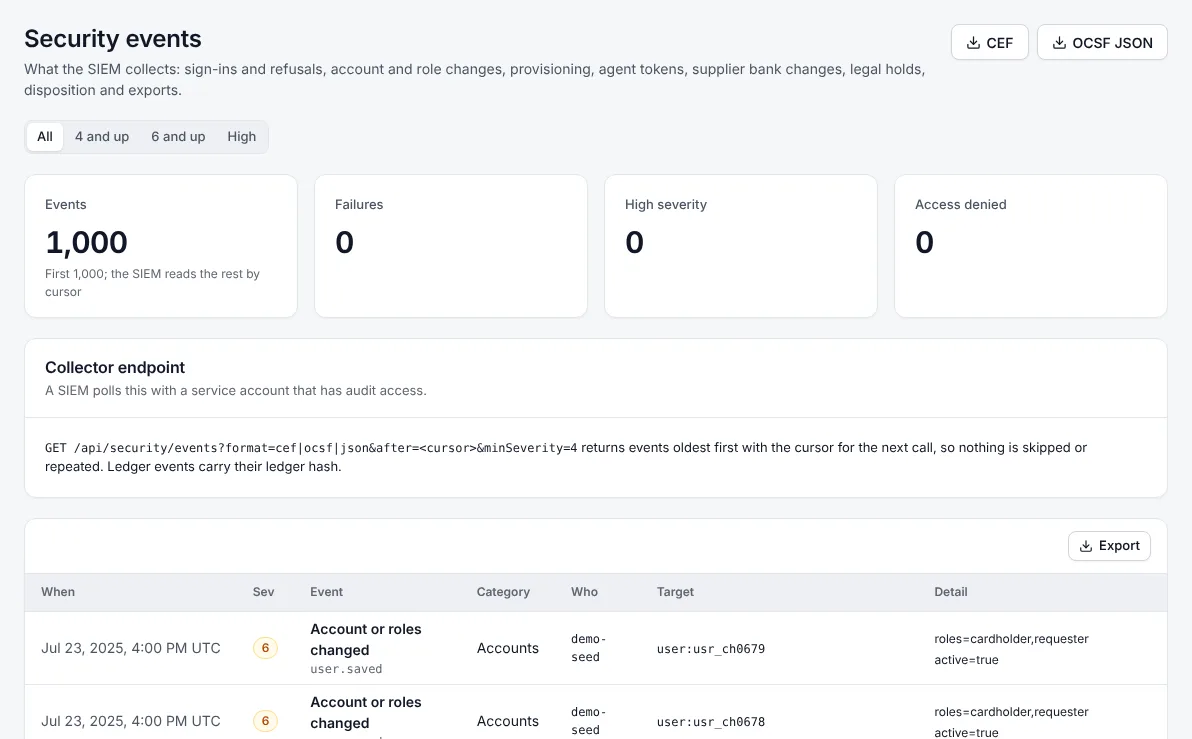
Single sign-on, SCIM, per-tenant encryption with your own KMS key, a hash-chained ledger signed hourly into your SIEM, and AI that never decides.
The problem
What gets in the way today
AI risk
Models that act on their own, or send sensitive documents outside.
Evidence on demand
Proving who did what, when, and that nobody changed it.
How Spend helps
Built in, not bolted on
Agents propose, people decide
Agents never approve, award, release payments or change policy. Every step is on the ledger.
Analytics and insightTamper-evident ledger
Hash chain, hourly signed checkpoints and a SIEM feed in JSON, CEF or OCSF.
Your keys, your exit
Bring your own KMS key; export everything at any time as NDJSON with a checksum.
Products for it, security and audit
See it on your own invoices
We run a bake-off on a sample of your real invoices and connect to a sandbox of your ERP, so you can judge the results before you sign anything.